


Introduction
There are two modes of operation on your Flutterwave account:
Test mode: No real money moves. Use test cards and bank accounts to try payments and payouts before you go live.
Live mode: Real payments and payouts. Switch to live mode only after you have tested the integration.
You can easily switch between Live and Test modes, by using the toggle button in the menu sidebar on your settings page. When you switch between modes, we'll also switch the API keys shown. Test keys will always have _TEST as prefix (for example, FLWPUBK_TEST-XXXXXXXXXXXXXXXXXXXXXXXXXXX-X)
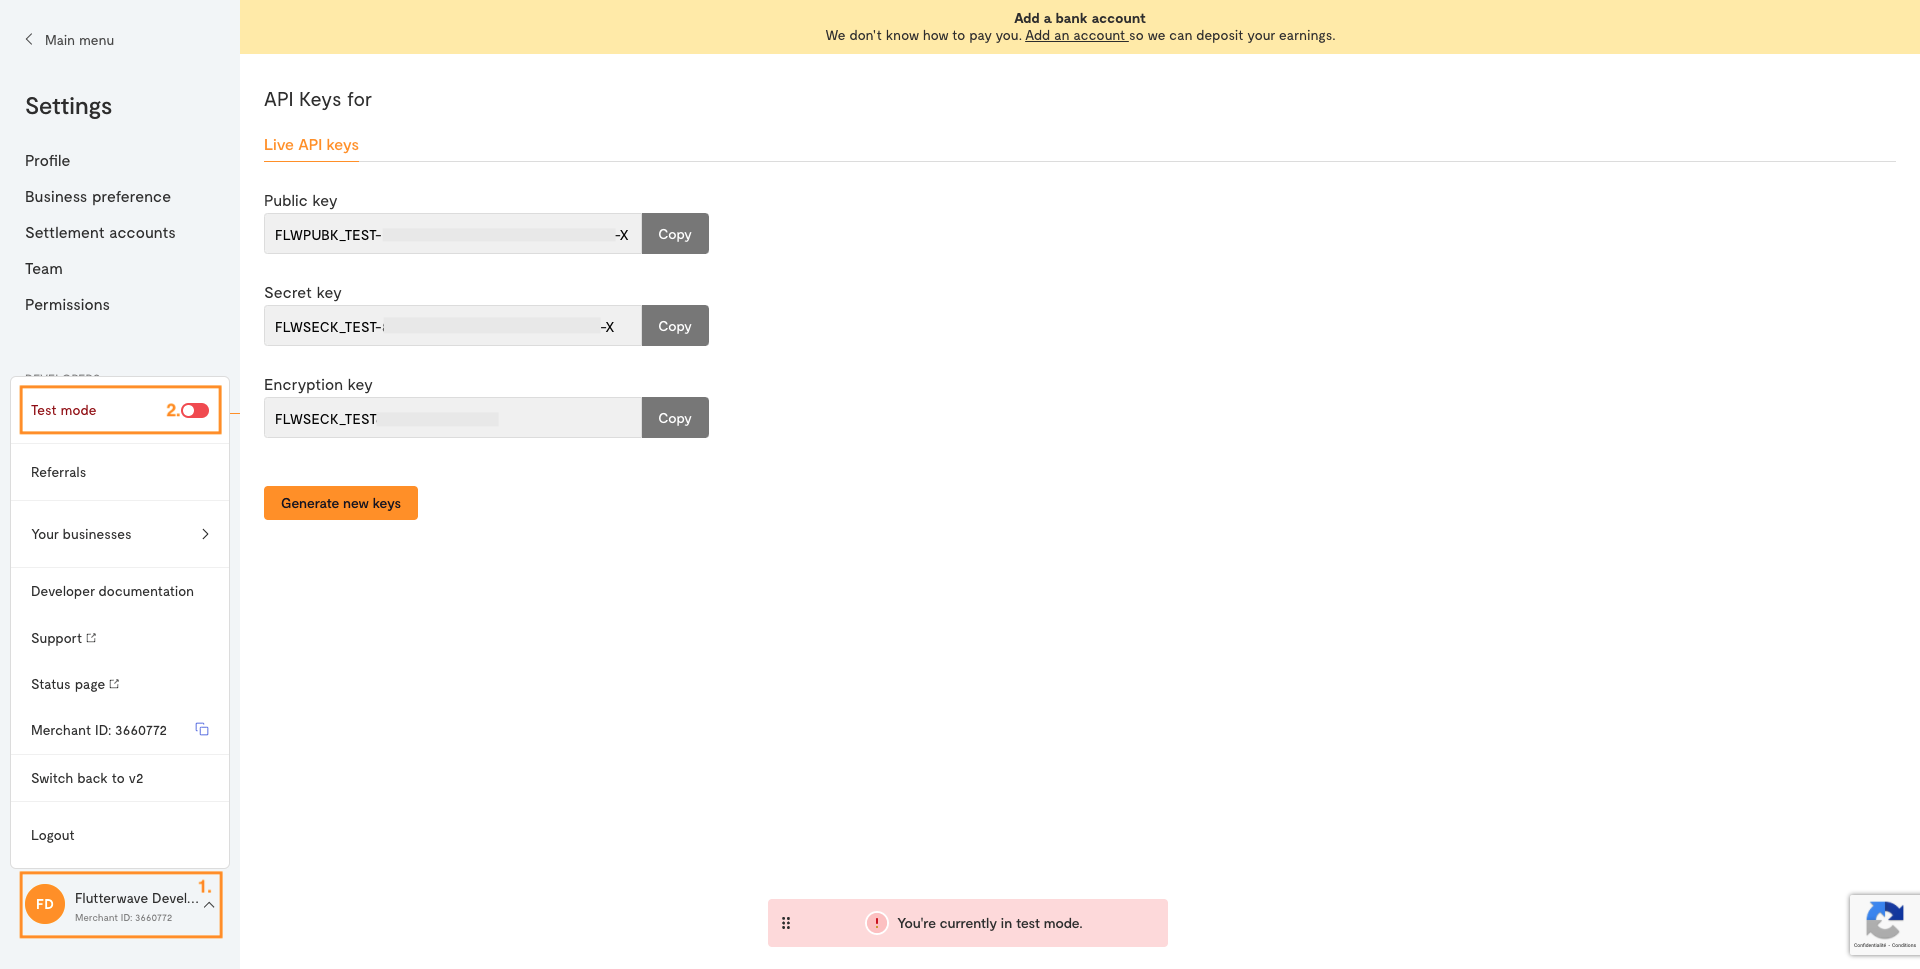
Get your API Keys
When you create a Flutterwave account, you receive three types of API keys:
Secret key: Grants full access to your account. Use it only in secure server-side environments. Never expose it publicly.
Public key: Safe for client-side use (e.g., Flutterwave Inline).
Encryption key: Required for encrypting payloads when using the direct card charge endpoints. See the encryption guide for more details.
Your API keys are essential for authenticating requests to our servers. To get your API keys:
- Log into your Flutterwave account
- Go to your dashboard.
- Navigate to Settings
- Select the API Keys menu under the DEVELOPERS section and copy your keys.
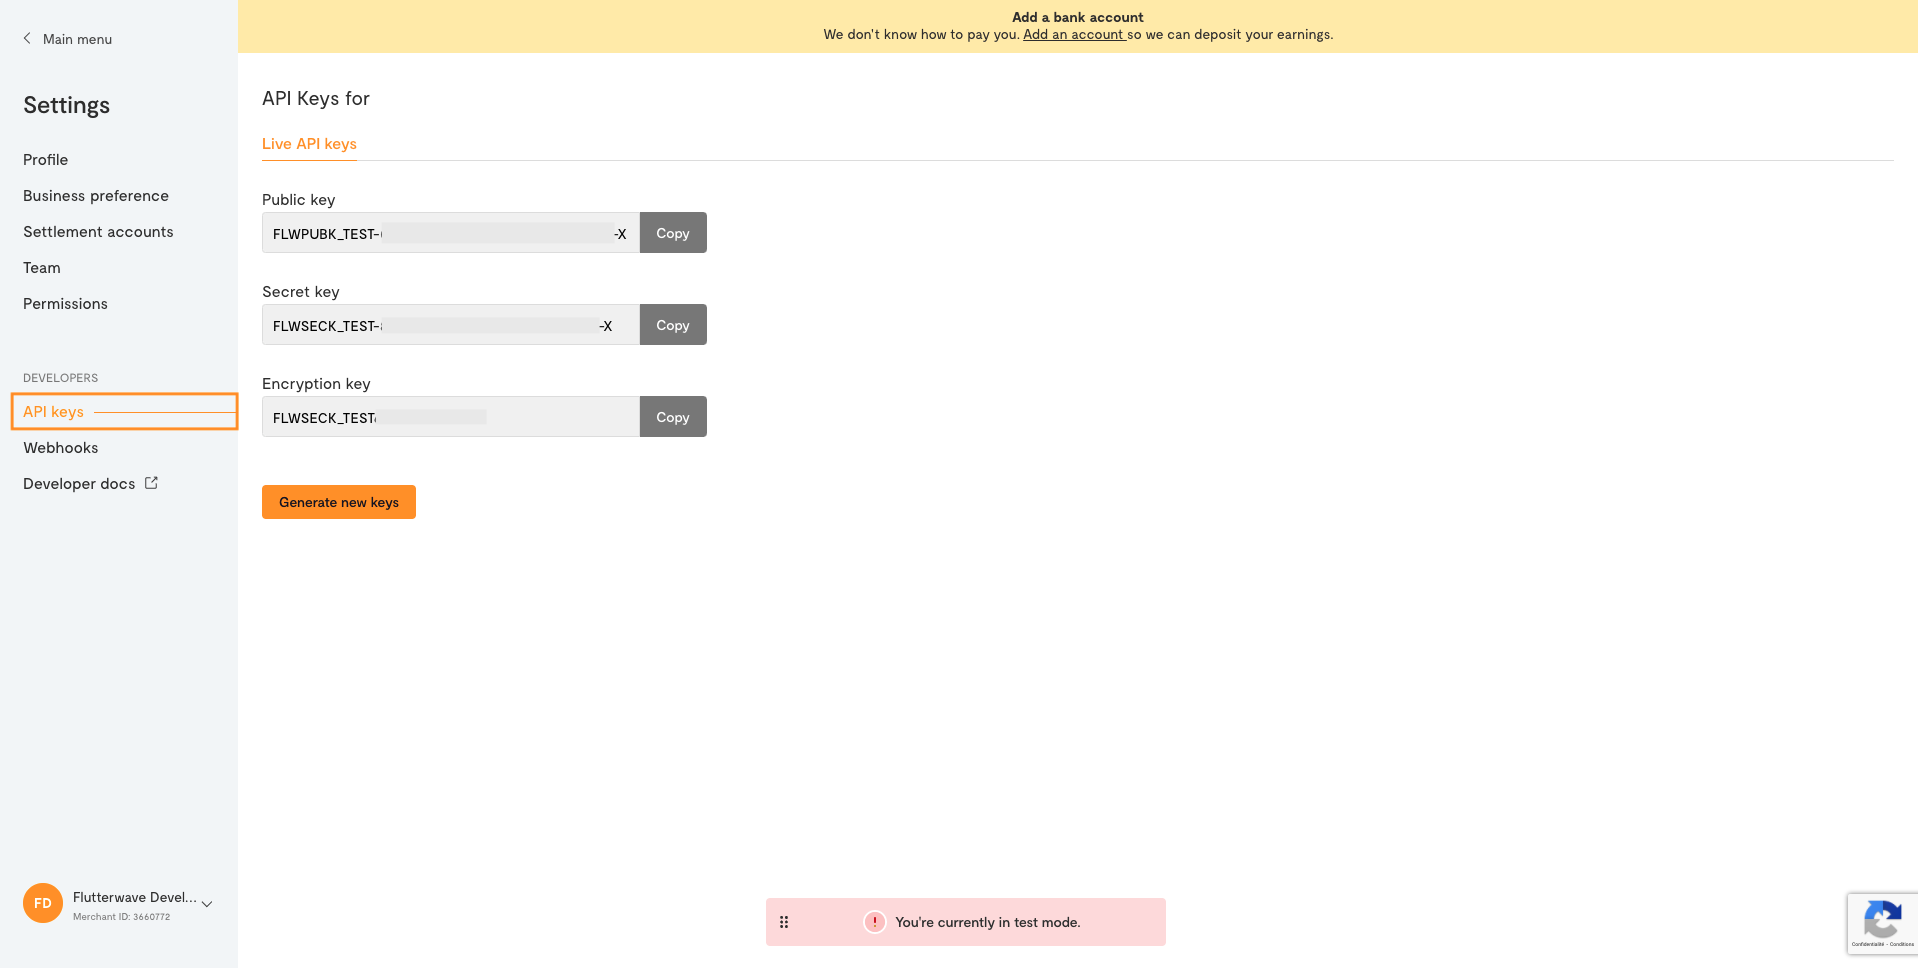
In the live environment, API key management is slightly different. To enhance the security of your live transactions, we mask the keys to prevent unauthorized access.
Don't Take Any Chances
If you think your keys may have been compromised (for instance, you accidentally committed them to Git), you should immediately generate new ones using the Generate new keys button on the Settings > API page on your dashboard.
This will invalidate all existing keys and give you a new set, and you can then update your app to use the new ones.
Authorizing API calls
All API calls on Flutterwave are protected by default. Any API requests made without proper authorization will result in the status code 401: Unauthorized.
Safeguard your API Key
Your secret key can perform any actions on your Flutterwave account without restriction. It should be kept confidential and only stored on your servers, preferably as an environment variable.
It should not be included in your Git repository or front-end JavaScript code.
Authorize server-side requests with your secret key. Set the Authorization header to Bearer YOUR_SECRET_KEY. There is no colon between Bearer and the key.
For example, an API call in Node.js would look like the following:
Javascript
const response = await fetch("https://api.flutterwave.com/v3/payments", {
  method: "POST",
  headers: {
    Authorization: `Bearer ${process.env.FLW_SECRET_KEY}`,
    "Content-Type": "application/json",
  },
  body: JSON.stringify({
    // Your payload
  }),
});
const body = await response.json();
If you're using one of our backend SDKs, you don't need to pass the header manually; instead, you'll provide your keys when initializing the library.
Javascript
// Install with: npm i flutterwave-node-v3
const Flutterwave = require("flutterwave-node-v3");

const flw = new Flutterwave(
  process.env.FLW_PUBLIC_KEY,
  process.env.FLW_SECRET_KEY
);

// Subsequent calls will automatically have the header added
flw.Misc.bvn({ bvn: "22222223883" }).then((response) => console.log(response));